
Blog posts tagged "security & compliance"
Canonical is pleased to share its latest research report, “The open source chain of trust.” Based on a survey of 500 DevOps professionals, the report...
Increasingly, enterprises are interested in improving their level of control over their data, achieving digital sovereignty, and even building their own...
Europe’s open source ecosystem is at a turning point. The Linux Foundation’s Open Source as Europe’s Strategic Advantage: Trends, Barriers, and Priorities for...
CMMC version 2.0 came into effect on December 26, 2023, and is designed to ensure adherence to rigorous cybersecurity policies and practices within the public...
With the latest LXD release, Ubuntu Pro now supports auto-attachment for LXD guest instances, offering organizations a seamless way to extend Ubuntu Pro...
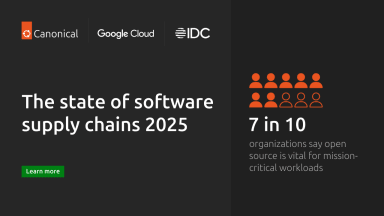
Open source software is a popular tool for businesses for many reasons, but this adoption has introduced new challenges in maintaining their open source...
The CRA is coming, and you need to be prepared. Depending on the Class your product falls into, there could be additional assessment, security, documentation,...
In this third and final part of the series, I’ll provide some tips on how to set up your roadmap and effectively demonstrate compliance without overburdening...
In my previous blog, we ran through what NIS2 is and who it applies to. In this second part of the series, I’ll break down the main requirements you’ll find...
The EU NIS2 directive, which calls for strengthening cybersecurity across the European Union, is now active in all member states. Join me for this 3-part blog...
Canonical CISO Stephanie Domas outlines the community response to the EU Cyber Resilience Act and explores how it will affect enterprises using open source software.
As Canonical approaches its 20th anniversary, we have proven our proficiency in managing a resilient software supply chain. But in the pursuit of excellence,...